Skip to content

In person · Spring 2027 · Kean University Union campus · College students only · Tentatively Saturday, January 16, 2027

Pre-register

learn

Beginner prep guide

Never played a CTF? Start here. Set up a few free tools, work through the practice track, and you'll be ready for Part I of every category. None of this is required, but each step makes the day easier.

a one-evening plan

If you only have an hour or two

  1. step_1

    Try the practice track

    Start with the practice box, then the seven practice challenges below it: one per category, each teaching that category's first move.

  2. step_2

    Do 3 practice problems

    Open the CyLab Security Academy challenge library (formerly picoGym) and start with the easiest ones. Read a write-up if you get stuck; that's how everyone learns.

  3. step_3

    Play OverTheWire Bandit 0 to 5

    Five short levels that teach you to move around a Linux shell and read files.

apt install

Tools worth installing

All free. Install them before the event so you aren't downloading a 400 MB file on venue Wi-Fi.

Kali Linux or WSL

A Linux command line

Many challenges are easier from a Linux shell. On Windows, install WSL (Windows Subsystem for Linux) with Ubuntu. On a Mac, the built-in Terminal covers most of it. Kali Linux in a virtual machine comes with lots of security tools pre-installed, but it's optional.

try: Run wsl --install in an admin PowerShell, reboot, then try ls, cat, file, and strings on a few files.

Wireshark

Network captures (Forensics)

Opens .pcap files so you can read network traffic packet by packet. Forensics challenges often hide a flag in a capture: a web request, a file transfer, or a chat message.

try: Open any sample capture, then right-click a packet and choose Follow > TCP Stream.

Ghidra

Reverse engineering

A free disassembler and decompiler from the NSA. Load a program and Ghidra turns machine code back into readable C-like code so you can see what it checks.

try: Load a small program, run auto-analysis, and find the main function in the Symbol Tree.

CyberChef

Decoding anything (Crypto, Misc)

A browser tool for chaining transforms: base64, hex, rot13, XOR, and hundreds more. Its Magic operation will even guess the encoding for you. Nothing to install.

try: Paste the puzzle from the practice box below into CyberChef and solve it there too.

Python

Scripting (every category)

When you need to try 1,000 keys or parse a weird file, a 10-line Python script beats doing it by hand. Learn variables, loops, strings, and bytes. That covers most CTF scripting.

try: Run python3 -c "print(bytes.fromhex('4b45414e').decode())" and see what it prints.

Your browser's DevTools

Web challenges

Press F12. The Elements, Network, Application (cookies), and Console tabs solve a surprising number of beginner web challenges.

try: Open DevTools on any site and look at its cookies under Application > Storage.

your first flag

Practice box

The input below is a flag wrapped in three layers of encoding. Peel them off one at a time.

  1. Pick a transform and look at the output.
  2. If it looks closer to readable text, click "Use output as input" and keep going.
  3. Base64 often ends in =. Hex is only 0-9 and a-f. Rot13 shifts every letter by 13.
  4. When you see something shaped like KEAN{...}, submit it.
Stuck? Show the answer

The order is base64 decode, hex decode, then rot13. The flag is KEAN{practice_makes_perfect}. It's a practice flag only and won't score anything on the real platform.

practice.sh (runs in your browser, nothing is sent)

transform

output

58524e417b63656e70677670725f7a6e7872665f637265737270677d

practice 1 to 7

Practice track

Seven tiny challenges, one per category. Each one teaches the first thing to try in that category. Everything runs on this site, and the flags are checked in your browser.

0 / 7 solved

Practice flags score nothing on the real platform. Your progress stays in this browser only.

  1. practice_1 · Web

    Bakery Backstage

    first move: view the page source

    The Copper Kettle Bakery (fictional) just launched a website. Developers sometimes leave notes in the HTML that the page never shows. Find both halves of the flag: each is labeled Flag part 1 of 2 or Flag part 2 of 2, and the full flag ends with }.

    Hint

    Press Ctrl+U (or right-click, View Page Source) to see the raw HTML, comments included. The second half is written inside a file that well-behaved search engines skip: robots.txt gives you its path, and you open that path to read it.

    Walkthrough (full spoilers)
    1. Open the bakery page and press Ctrl+U (on a Mac: Cmd+Option+U). You can also press F12 and look in the Elements tab. On an Android phone, put view-source: in front of the page address in Chrome.
    2. Find the HTML comment that starts with <!--. It holds part 1 of the flag and points you to robots.txt.
    3. Open /practice/web/robots.txt. It lists one Disallow: path: a file the bakery hoped nobody would read.
    4. Open that path in your browser (the page address is /practice/web/kitchen-notes.txt). The path itself isn't the flag: part 2 is the line labeled Flag part 2 of 2 inside the file. Join the two parts with nothing in between, so the flag ends with }.
    5. On real sites, robots.txt lives at the root, for example example.com/robots.txt. Checking it is a classic first move in Web challenges.

    free tools: Chrome DevTools docs (opens in a new tab)
  2. practice_2 · Crypto

    Lantern Club Letters

    first move: use known plaintext

    The Lantern Club (fictional) scrambles its messages by shifting every letter the same number of places. Members always open with the password KEAN. You intercepted RLHU{wyhjapjl_ruvdu_wshpualea_dpuz}.

    Hint

    If the message must start with KEAN, compare it with the first four letters you intercepted. How far is K from R?

    Walkthrough (full spoilers)
    1. A shift cipher (a Caesar cipher) moves each letter forward by the same amount and leaves {, } and _ alone.
    2. You know the plaintext starts with KEAN and the ciphertext starts with RLHU. Count from K to R: L, M, N, O, P, Q, R is 7 steps.
    3. Check the other letters: E to L is 7, A to H is 7, N to U is 7. The key is 7.
    4. Shift every letter back by 7. In CyberChef, use the ROT13 operation and set Amount to 19 (26 minus 7), or -7.
    5. Knowing (or guessing) part of the plaintext, called a crib, is how most classical ciphers fall.

    free tools: CyberChef (opens in a new tab)

  3. practice_3 · Forensics

    The Report That Won't Open

    first move: check the magic bytes

    An intern at Gearloft Supply Co. (fictional) emailed you q3-report.pdf, but no PDF reader will open it. Figure out what the file really is.

    Hint

    Real PDF files start with the bytes %PDF. Look at the first few bytes of this one. What starts with PK?

    Walkthrough (full spoilers)
    1. Never trust a file extension. Look at the file's first bytes, its magic bytes, instead.
    2. On Linux, macOS or WSL run file q3-report.pdf. Or drop it into CyberChef and use the Detect File Type operation.
    3. Both say it's a ZIP archive: it starts with PK (the bytes 50 4B 03 04).
    4. Rename it to q3-report.zip and open it, or run unzip q3-report.pdf. On Windows, if you can't see the .pdf ending, turn on File Explorer's View, Show, File name extensions first.
    5. Read q3-report.txt inside. The auditor's note at the bottom is the flag.

    free tools: CyberChef (opens in a new tab), List of file signatures (opens in a new tab)

  4. practice_4 · OSINT

    New Year's Sunrise?

    first move: read the photo's metadata

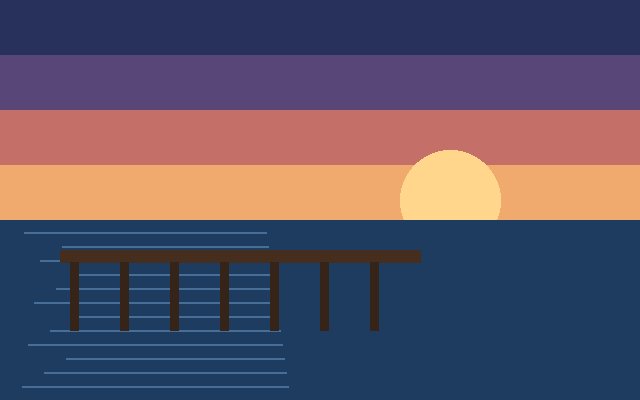
    A (fictional) photographer, Dana Whitlock, posted pier-sunrise.jpg and claimed it was the first sunrise of 2026, on New Year's Day. Use the photo itself to find the date it was really taken. Submit it as KEAN{practice_YYYY_MM_DD}.

    Hint

    Cameras save hidden details inside every photo, called EXIF metadata. Some of the dates in there mean "when the file was edited", not "when the photo was taken".

    Walkthrough (full spoilers)
    1. Download the original file (screenshots and many upload sites strip metadata).
    2. Run exiftool pier-sunrise.jpg. No install? On Windows, right-click the file, Properties, Details: Date taken is the camera's date. Or use any online EXIF viewer.
    3. You'll see two different dates. Modify Date (2026:01:01) is when the file was last saved by editing software.
    4. Date/Time Original is when the camera's shutter fired. That's the real date.
    5. Write that date as KEAN{practice_YYYY_MM_DD} with underscores, for example 2024:03:09 becomes practice_2024_03_09.

    free tools: ExifTool (opens in a new tab)

  5. practice_5 · Reverse Engineering

    Arcade Ticket Checker

    first move: read the code and run it backwards

    The Gearloft Arcade (fictional) checks prize-ticket codes with a tiny Python script. The right code isn't stored anywhere in it, only a scrambled version. Work out which code passes the check.

    Hint

    scramble() XORs each character with 0x21 and then adds its position i. Undo the steps in reverse order: subtract i first, then XOR with 0x21 again.

    Walkthrough (full spoilers)
    1. Reverse engineering starts with reading: find where the input is checked. Here it's scramble(guess) == TARGET.
    2. scramble() turns character number i into (ord(ch) ^ 0x21) + i.
    3. To undo it, take each number n in TARGET at position i, subtract i, then XOR with 0x21 (XOR undoes itself), then turn it back into a character with chr().
    4. In Python: print(''.join(chr((n - i) ^ 0x21) for i, n in enumerate(TARGET))) after pasting in the TARGET list. No Python installed? Paste both lines into the Pyodide console, which runs Python in your browser.
    5. Run python checker.py and paste your answer to confirm it says Prize unlocked.

    free tools: Python (opens in a new tab), Pyodide console (Python in the browser) (opens in a new tab)

  6. practice_6 · Steganography

    Nothing to See Here

    first move: look at the bit planes

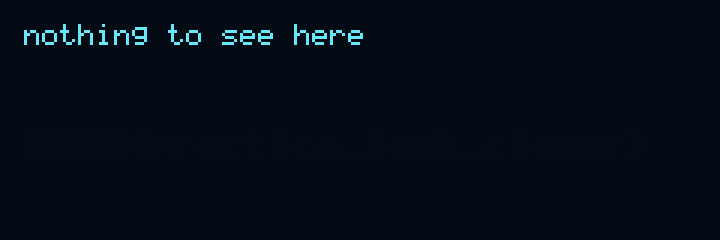
    This picture of a night sky says there's nothing to see. Some of its pixels disagree: they're just one or two shades away from the background, far too close for your eyes to notice.

    Hint

    Computers see the exact color of every pixel, even when you can't. Look at the image one bit at a time (its bit planes), or recolor every pixel that is exactly the background color.

    Walkthrough (full spoilers)
    1. Each pixel's color is three numbers (red, green, blue). The background here is (5, 11, 20) and the hidden text is one step lighter. Your eyes can't tell, but the bits can.
    2. Open StegOnline, upload night-sky.png, and choose Browse Bit Planes. Look at Red 0, the lowest bit of the red channel: the hidden text shows up in black and white.
    3. No upload? In Photopea, pick the Paint Bucket, set Tolerance to 0, untick Contiguous, and click the background with a bright color. Only exact-background pixels change, so the text stands out.
    4. Read the text letter by letter. That's the flag. Like every flag, it starts with KEAN{ and ends with } (curly braces, not parentheses).
    5. This is the first steg move: look past what the image shows, at what its pixels and bytes actually hold.

    free tools: Photopea (free, in the browser) (opens in a new tab), StegOnline (opens in a new tab)

  7. practice_7 · Misc

    Night Radio

    first move: recognize the encoding

    The Harbor Light Radio Club (fictional) logged a strange transmission at 22:43. Decode it. The flag is KEAN{practice_ + the decoded words in lowercase, joined with underscores + }.

    Hint

    Only dots, dashes, spaces and slashes. That alphabet was made for radio and telegraphs.

    Walkthrough (full spoilers)
    1. The first move in Misc is naming the encoding. Dots and dashes with / between words is Morse code.
    2. Paste the line into CyberChef and use From Morse Code (the default settings expect a space between letters and / between words).
    3. You get three words in capitals. Make them lowercase and join them with underscores.
    4. Wrap them as the prompt says: KEAN{practice_ + your words + }.

    free tools: CyberChef (opens in a new tab)